By Eagle Tech Corp • October 2026 • 7-minute read
Quick Answer
Quick Answer: More security tools do not automatically mean better protection. Many nonprofits build their cybersecurity one purchase at a time: a donated license, a grant-funded product, a fix for an insurance question, a suggestion from a board member. Over time, that creates overlap in some areas, gaps in others, and alerts nobody is reviewing. Strong cybersecurity works like an immune system, a coordinated set of safeguards, people, and processes, rather than a medicine cabinet full of individual remedies.
For nonprofits across Northern Virginia, Maryland, and Washington, DC working with lean teams and donor-funded budgets, a simple annual check-up of what you have, why you have it, and who is watching it is often more valuable than adding the next tool.
Key Takeaways
- A long list of security products can look like strong protection without actually providing it.
- Tools added one at a time often overlap in some areas and leave gaps in others.
- An alert that nobody reviews offers almost no protection.
- Staff and volunteers are part of the system, so they need clear expectations, not just software.
- Your security should be re-evaluated as your programs, people, and systems change.
Boardroom Brief
Executive directors and board members do not need to understand every technical detail to lead on this.
Ask a simpler question:
Can someone explain, in plain language, what each of our security tools does and why we pay for it?
Think about every security subscription, license, and service your organization currently uses, including anything donated or funded through a grant.
If nobody can answer clearly, that is not a failure. It is a sign the system grew over time and has never been reviewed as a whole.
A Medicine Cabinet Is Not a Health Plan
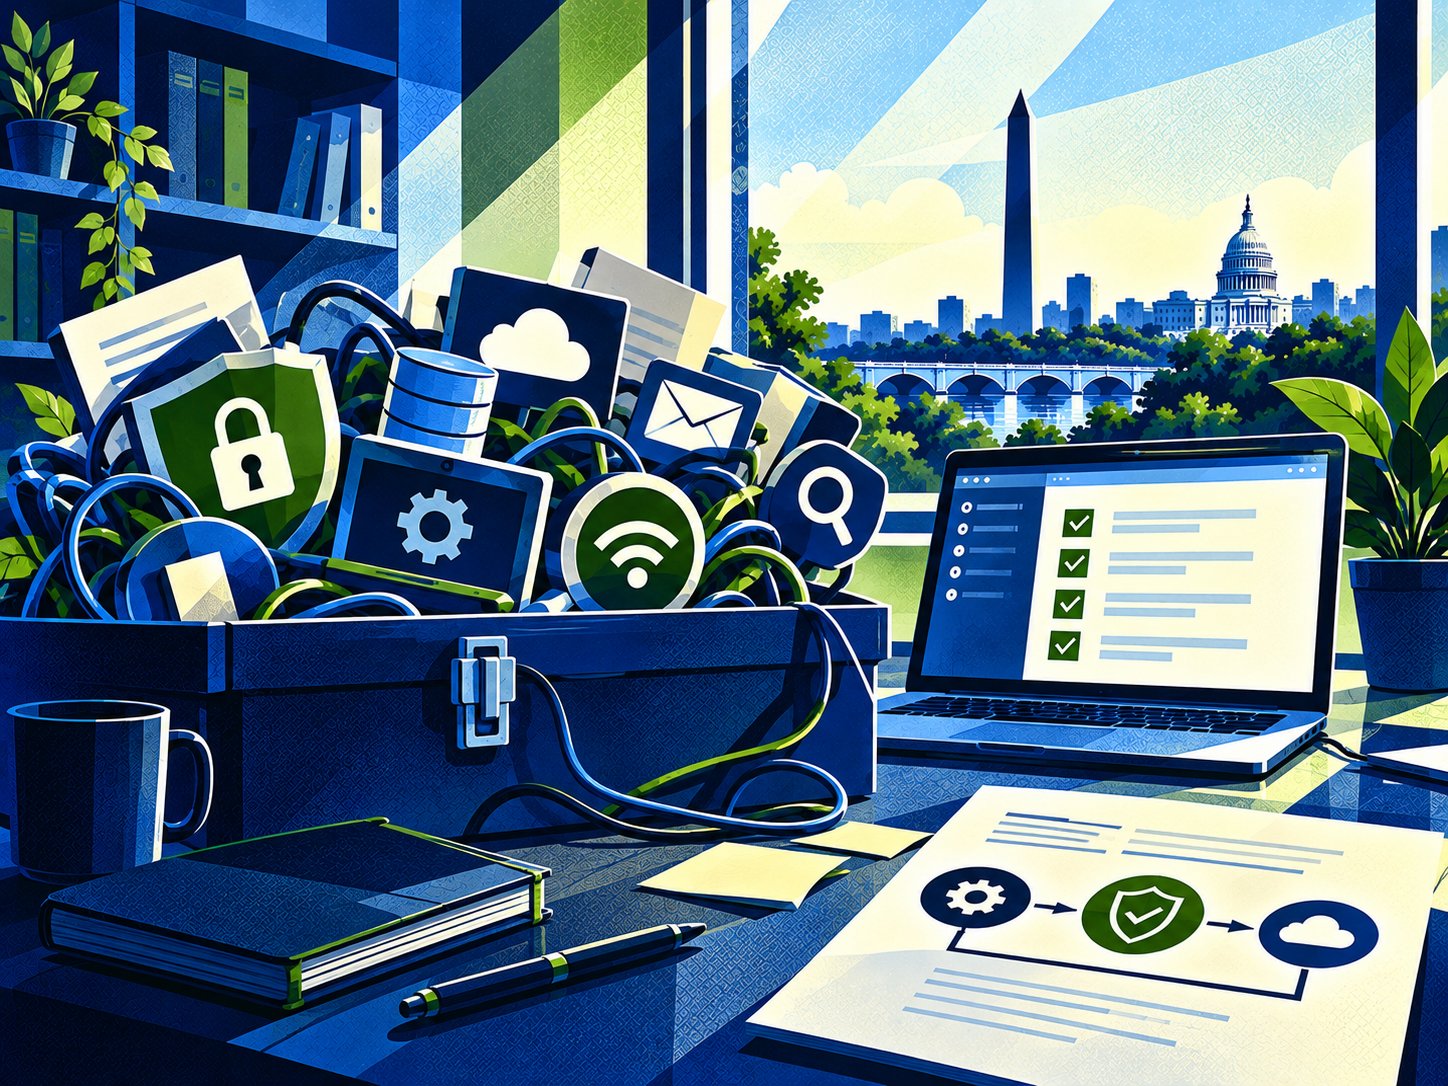
Every autumn, the medicine cabinet gets a little more crowded. Cold medicine left from last winter, vitamins bought in bulk, half-used bottles of cough syrup, and a prescription that should have been thrown out months ago. There is plenty of medicine there, but a full cabinet has never been a measure of anyone’s health.
Nonprofit cybersecurity can end up in the same place. A phishing scare prompts one purchase. A cyber insurance application leads to another. A technology grant funds a third, and a board member recommends a fourth. Each decision made sense at the time.
The more useful question now is whether those pieces actually protect your organization together, and whether your team knows what to do with them.
Do More Security Tools Mean Better Protection?
The truth: more tools only help when each one has a clear purpose and they work together.
It is an easy assumption to make. If one product adds protection, adding another should make the organization even safer. But that is where the myth starts to break down.
Layered protection can be valuable when it is designed on purpose. When it simply accumulates, it tends to create three problems: paying twice for the same protection, missing protection no one realized was needed, and more complexity than a small team can realistically manage. For a nonprofit, that third problem matters most, because complexity is what causes alerts to go unread and settings to go unchecked.
Why Do Nonprofits Accumulate Security Tools?
The truth: most nonprofit security stacks are built reactively, one need at a time.
Nonprofits often acquire technology differently from businesses. Tools arrive through donated or discounted licenses, grant budgets with specific spending rules, vendor recommendations, volunteer expertise, and requirements from funders or insurers. Staff turnover adds another layer, because the person who chose a tool may no longer be there to explain why.
None of this is a mistake. It is how resource-constrained organizations operate. But it means the full picture is rarely designed by anyone. It simply grows.
How Should Nonprofit Cybersecurity Work?
The truth: healthy cybersecurity works like an immune system, not a shelf of remedies.
An immune system is a coordinated set of defenses that recognizes problems and responds to them. Your organization’s cybersecurity should work the same way, with three parts that support each other:
- Safeguards that complement each other rather than simply coexist
- People, including staff and volunteers, who understand what is expected of them
- Process, a clear plan for who responds when something suspicious happens
Security tools are one part of that system. They are most effective when they fit the way your organization actually works and protect what matters most to your mission, especially donor, client, and financial data.
How Can a Nonprofit Give Its Cybersecurity a Check-Up?
You do not need to understand the technical details of every product your organization uses. You should be able to get clear answers to four basic questions.
1. What are we currently using, and why?
Someone on your team or a trusted outside partner should be able to explain what each major protection does and why it is there. Include donated and grant-funded tools, which are often the easiest to lose track of.
2. Where do our protections overlap, and where are the gaps?
Overlap is not automatically a problem. Sometimes layered protection is intentional. What matters is knowing whether your approach was designed that way or simply grew without coordination.
3. Who is making sure everything is working?
A tool can generate alerts around the clock, but that does not help much if nobody reviews them or knows what should happen next. In a small nonprofit, this responsibility often falls through the cracks between staff, volunteers, and outside vendors.
4. When did we last re-evaluate what we need?
Organizations change. Staff and volunteers come and go, new programs launch, new applications get adopted, and funders or insurers raise their expectations. Security that made sense three years ago may no longer fit the organization you are today.
Eagle Insight
Five questions worth answering internally with your leadership team. These are for your own conversation.
- Do we have a single list of every security tool, license, and subscription we pay for or receive?
- Which of those tools came from a grant or donation, and what happens when that funding ends?
- Who reviews security alerts today, including evenings and weekends?
- Would our current tools support the answers on our cyber insurance application?
- Do former staff and volunteers still have access to any of these systems?
If several of these are hard to answer, that is useful information on its own.
A 5-Point Security Check-Up
Use this as a discussion framework for leadership and operations staff.
- Inventory: Do we know every security tool we have and what it does?
- Purpose: Does each tool solve a specific, current need?
- Coverage: Do we know where protections overlap and where gaps exist?
- Ownership: Is a named person or partner responsible for reviewing alerts?
- Review: Have we re-evaluated our security in the last 12 months?
There is no score here. The goal is to see clearly what is working, what is redundant, and what is missing.
AI Consideration
Many security and productivity tools now include AI features, often turned on by default in a software update. That adds a new item to your check-up: knowing which tools process your organization’s data with AI, and what data they can reach.
Donor records, client information, and financial data deserve particular attention. Before adding another AI-enabled tool, it is worth confirming how it fits with what you already have and what information it is allowed to use.
Frequently Asked Questions
Do more cybersecurity tools make a nonprofit more secure?
Not necessarily. Additional tools help only when each one serves a clear purpose and works with the others. Tools added one at a time often create overlap, gaps, and more complexity than a small team can manage.
Why do nonprofits end up with too many security tools?
Nonprofits often acquire tools reactively, through donated licenses, grant-funded purchases, insurance requirements, and vendor or volunteer recommendations. Staff turnover can leave nobody who remembers why each tool was chosen.
How often should a nonprofit review its cybersecurity tools?
At least once a year, and whenever staff, programs, systems, or funding change significantly. A review should confirm what each tool does, where gaps exist, and who is responsible for monitoring alerts.
What happens if nobody reviews security alerts?
Unreviewed alerts provide little protection. Suspicious activity can go unnoticed until it becomes a serious incident. Every nonprofit should have a named person or partner responsible for reviewing alerts and responding.
What should a nonprofit cybersecurity check-up include?
An inventory of all security tools and their purpose, a review of overlaps and gaps, confirmation of who monitors alerts, a check of user access including former staff and volunteers, and a comparison against current insurance and funder requirements.
Who helps nonprofits in Northern Virginia, Maryland, and Washington, DC review their cybersecurity?
Eagle Tech Corp, based in Springfield, Virginia, provides managed IT and cybersecurity services for nonprofits throughout Northern Virginia, Maryland, and Washington, DC, with support available in English and Spanish.
About Eagle Tech Corp
Eagle Tech Corp provides proactive Managed IT services, cybersecurity solutions, Microsoft 365 management, and strategic technology consulting for nonprofit organizations throughout Northern Virginia, Maryland, and Washington, DC.
Founded by Eduard Lavilla, former CTO of the Organization of American States, and serving the DC Metro area since 2012, we help nonprofits protect donor and client data, make sense of the technology they already have, and explain it in clear, practical language, with assistance available in English and Spanish.
Get a Clearer View of Your Cybersecurity
A full medicine cabinet is not the same as good health, and a long list of security tools is not the same as good protection. What matters is whether the pieces work together for the organization you are today.
Stepping back to see the full picture is hard to do from the inside. If you would like a second set of eyes on what you already have, what overlaps, and what may be missing, we are glad to help.
Send us a note through the contact form, with no pressure and nothing to prepare in advance.